Security and controls
Govern access, approvals, and AI-driven execution.
Movo applies role-based and facility-based access controls, configurable approval policies, and an audit trail for every action.

AI approval controls
Configure approval requirements for AI-generated actions.
Conductor prepares proposed changes and executes them according to the policies defined for each workflow.
Conductor drafts
Conductor prepares the order, appointment, and reply without writing to connected systems.
Movo validates
Movo checks the proposed changes against current WMS data and dock capacity.
Policy governs execution
Each action is routed for authorized review or automatic execution according to the configured policy.
Movo executes and records
Movo carries out the authorized action and records the actor and the result.
Role-based access
Scope access by role and facility.
Permissions are limited to the user’s operating role and assigned facility.

Office
Access to scheduling, yard operations, Conductor, and reporting.
Dispatch
Read-only visibility across the assigned facility network.
Dock and gate
Terminal access limited to one facility and operating role.
Driver
Self-service check-in only, with no access to facility operations.
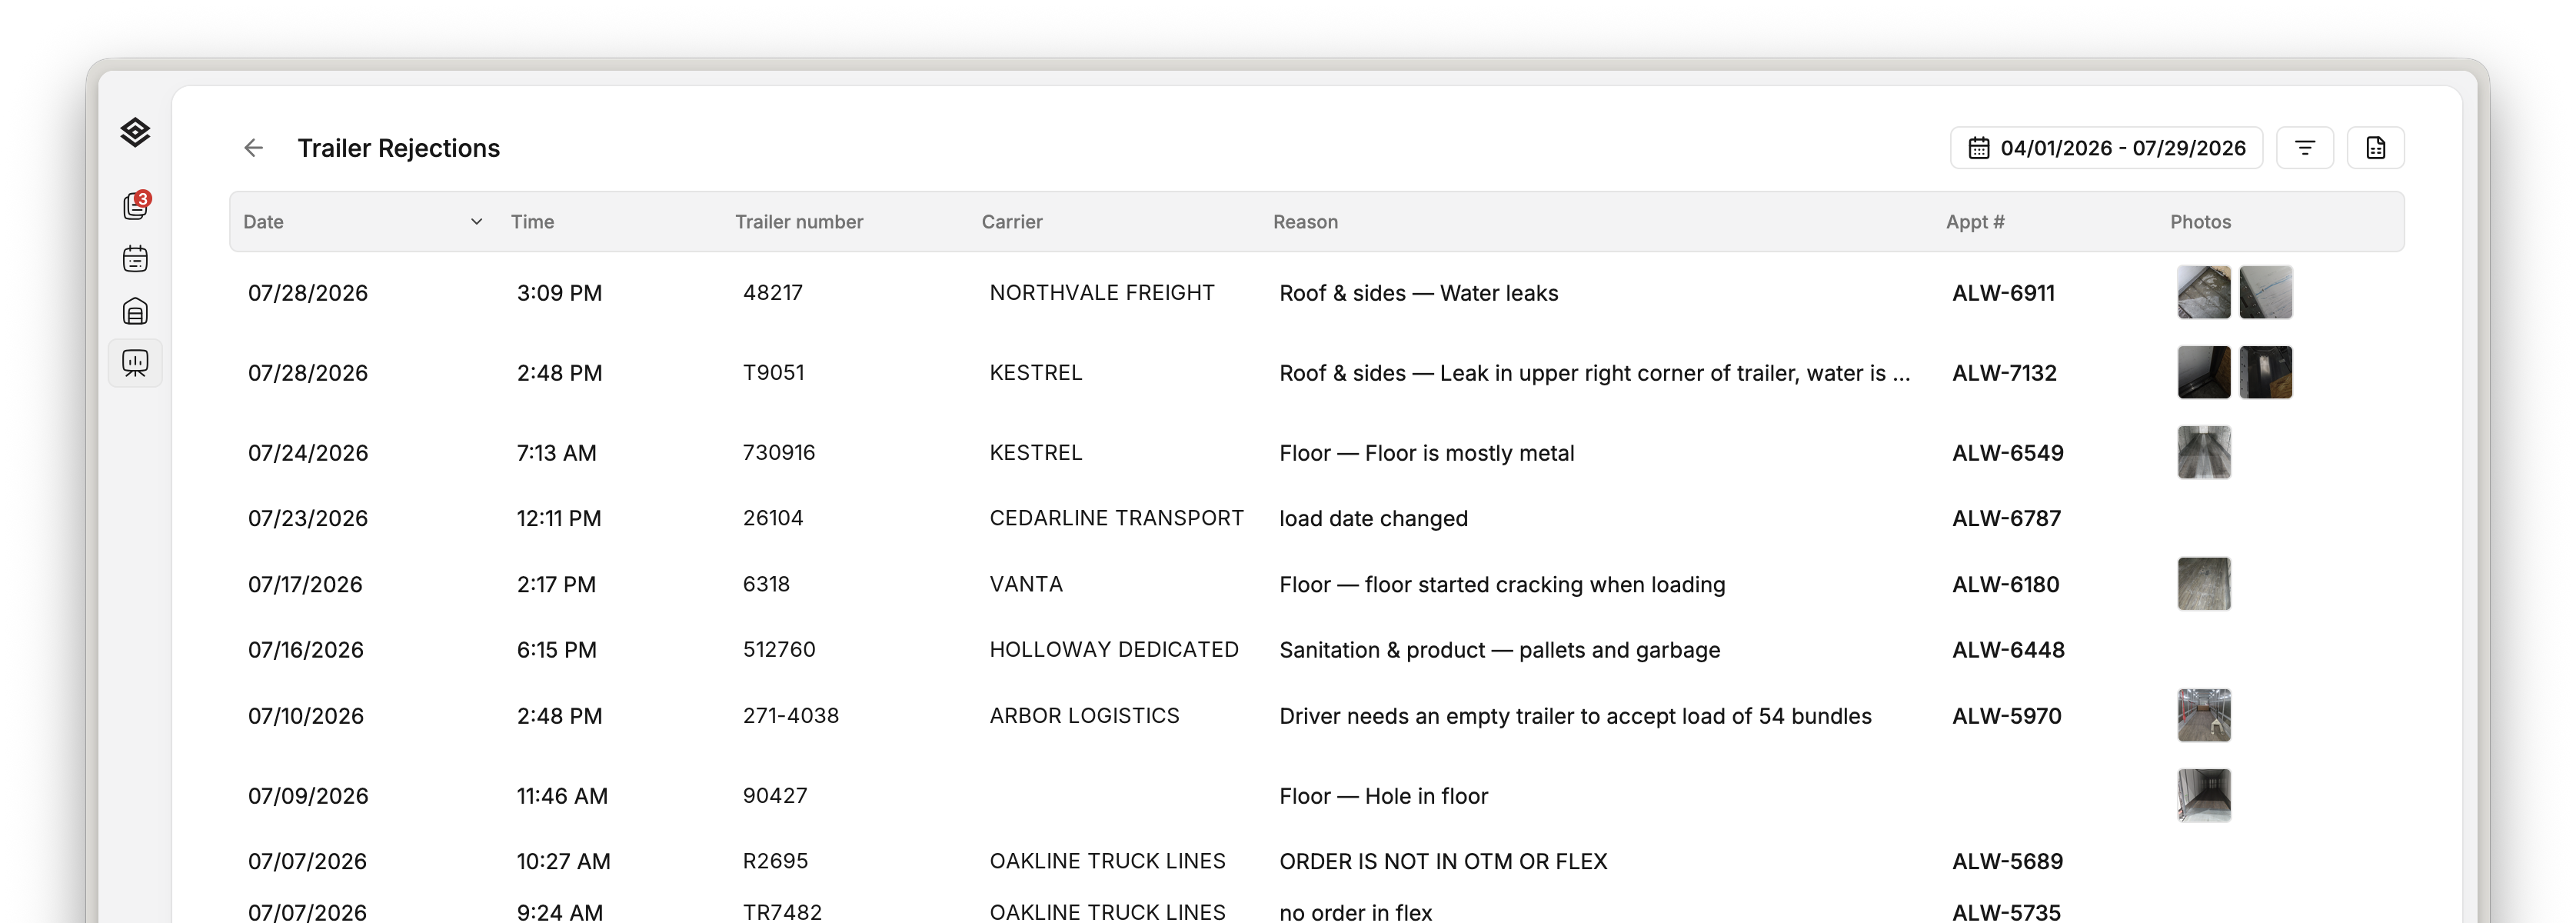
Audit trail
Preserve an audit trail for every change.
Movo records the actor, action, timestamp, and supporting reason or evidence.
Platform controls
Infrastructure and data protection controls.
Movo is hosted on AWS in the United States. Detailed architecture and control documentation is available during the technical security review.
- HostingAWS, United States
- Data in transitEncrypted
- Documents at restEncrypted and versioned
- PasswordsSalted password hashes; plaintext passwords are not stored or logged
- Credential managementSecrets are stored in managed secret storage. Deployment credentials are short-lived and are not stored in source code.
- Security monitoringApplication and infrastructure activity is monitored and logged.